
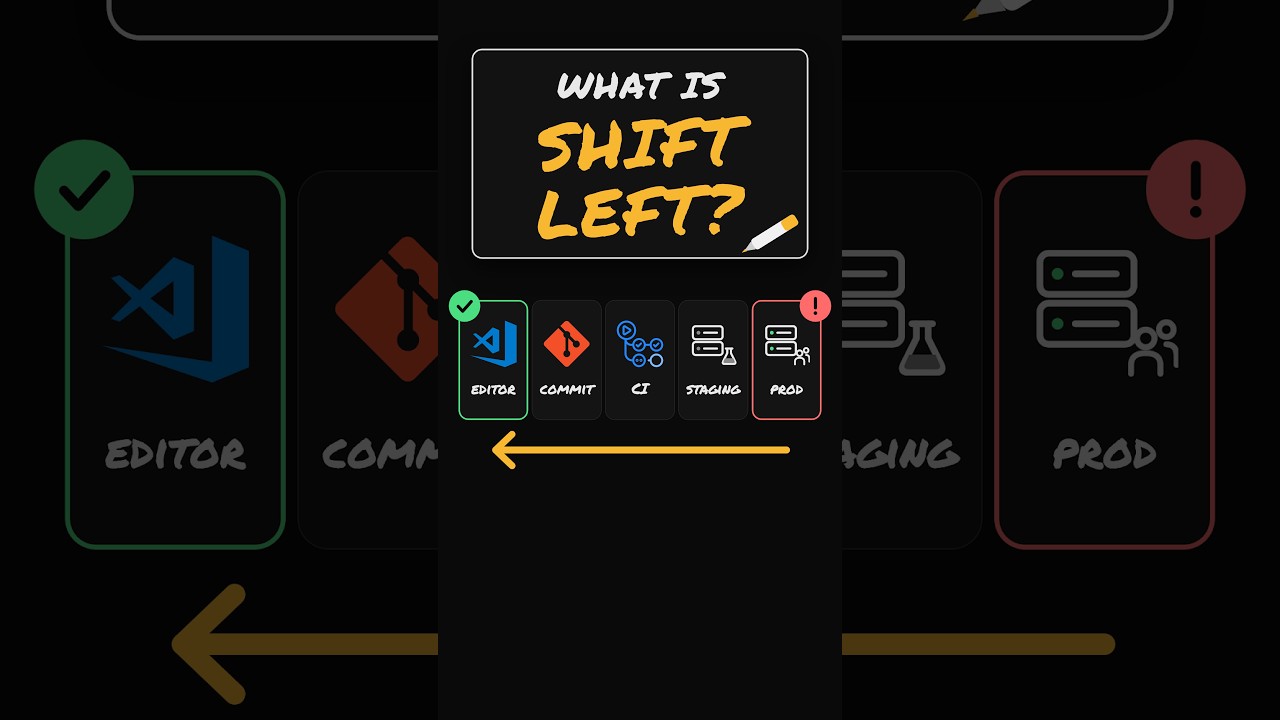
Shift Left Explained with SQL Injection Bug🐛
Shift Left Security, Explained! Shift left is the practice of moving security checks earlier in the software delivery line so issues get caught before code reaches production. SAST (static application security testing) scans code without running it, like CodeQL in a CI pipeline.
By KodeKloudKodeKloud
Read the full story
Originally published by KodeKloud on Oct 6, 2026.
Comments
Sign in to join the discussion.