
Citrix gives NetScaler admins another critical reason to patch
No word on exploitation status, but a 9.5 severity score suggests time is of the essence
The Register5 min read
5 stories
No word on exploitation status, but a 9.5 severity score suggests time is of the essence
The new vuln, CVE-2026-88779, is a memory overflow bug that leads to denial of service
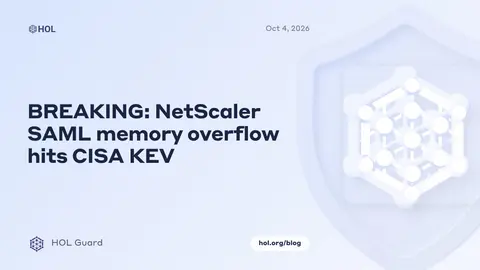
How to fix CVE-2026-88779: upgrade NetScaler ADC/Gateway to 14.1-73.41 or 13.1-64.28. Same-day CISA KEV on NetScaler SAML memory-overflow DoS.
Two questions remain: who is abusing the CVEs? And why did Citrix take so long to disclose?
How to fix CVE-2026-88771: upgrade NetScaler ADC/Gateway to 14.1-73.37 or 13.1-64.23
Showing 5 of 5 stories
You're all caught up.
Get the top AI news and tools straight to your inbox every week.
Weekly · AI news
Join 15,000+ AI enthusiasts