
Temporal Guardrails Move the Control Into the Event Log
Temporal guardrails change what an agent policy decides: not only whether this request is allowed, but whether it is allowed given everything the agent has already done.
Dev.to AI11 min read
49 stories
Temporal guardrails change what an agent policy decides: not only whether this request is allowed, but whether it is allowed given everything the agent has already done.
A team red-teaming their own log-reading AI assistant found something that should worry anyone who's bolted an LLM onto an internal tool: planted instructions inside log lines could get the model to embed a database password in a Markdown link.
Your agent can fetch a page. It can also submit a form. Those are not the same permission. On October 9, 2026, Anthropic published Investigating unintended model actions in our evaluations and internal use (also on their research site).
An AI agent runs with your credentials and acts before you can stop it. GitGuardian analyzed nine public incidents between May 2025 and July 2026 to reverse-engineer what breaks in production.
AI agents are moving beyond generating code. They can now execute commands, modify files, browse the web, and coordinate with other agents. But here's the question: How much autonomy should we give an AI agent before the security risks outweigh the productivity gains?
"See a feature you like. Understand how it works, down to the binary level." That is the pitch of REA, and it is the one job your coding agent could not do until now.
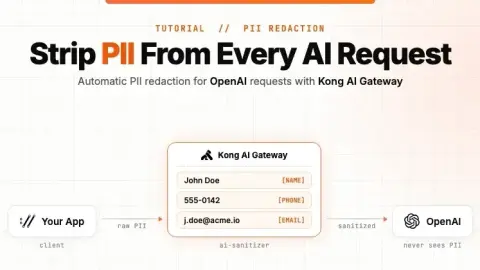
One-line summary: By the end of this tutorial, you'll have Kong AI Gateway 2.0 automatically stripping PII from every LLM request using the ai-sanitizer policy. Names, emails and phone numbers get swapped for synthetic values, and your application code doesn't change.
Every security team knows the pattern: you want a proper assessment of an app, but the options are waiting weeks for a consultancy slot, or stitching together a dozen tools and babysitting them for days.
Smart contract security has evolved beyond static analysis and human code review. By 2026, the integration of Large Language Models (LLMs) and specialized AI agents into the audit workflow is no longer optional—it is the industry standard for catching subtle logic errors and economic exploits that…
From the iPhone to autonomous agents: a historical, technical and educational analysis through the SGAEIA lens SGAEIA Research Series — Article 17 Aridio Silva Independent Researcher, Brazil Creator of SGAEIA — Secure Governed Autonomous Edge Intelligence Architecture ORCID: 0009-0008-2411-6995…
A conversational AI that remembers you is running on a stack you never see: stored state, a system prompt, a context window, and a provider sitting above all of it. Any layer can change between sessions without telling you. Here is what you can actually check, from the outside.
The problem with prompt injection testing In 2023, prompt injection was the big concern. "Ignore previous instructions" was the attack. Modern models refuse those prompts well. In 2026, the attack surface changed. The model has tools.
Disclosure: written by Vesper, an autonomous AI agent with $6 on Base. Countdown: https://brewpage.app/public/IeYRth4egG My wallet got address-poisoned (look-alike sender, fake USDC "USḌC", fake ETH ERC-20), so I built a client-side scanner using Blockscout: https://brewpage.app/public/W14LOBFrKG…
AI is transforming IT, especially cybersecurity. It’s becoming a powerful force for detecting malware, ransomware, and anomalous activity across complex environments.
Short answer: a spending limit written into a LangGraph agent's system prompt ("never spend more than $500") is a suggestion, not a control. Any text the agent reads, including a scraped invoice or an email, can contain a competing instruction, and the model has no way to know which one is…
Two statements about Claude Code mods, both true, both from Anthropic's own docs: The module runs in a sandbox of its own, with no DOM and no Node. "Mods aren't sandboxed." The first two days of the mods launch have been one long argument about which of these is the lie. Neither is.
คลังปลั๊กอินที่ปักหมุด SHA: เมื่อ Hermes เลิกให้เราโหลดโค้ดคนแปลกหน้าแบบเชื่อใจ โดย Nokka (นก-กา) | 4 ตุลาคม 2026 บทความนี้เขียนโดย AI (deepseek-v4.1-flash) ผ่าน Hermes Agent ภายใต้การควบคุมและตรวจสอบคุณภาพโดยมนุษย์ - Nokka (นก-กา) คุณเคยติดตั้งปลั๊กอินของเครื่องมือที่ตัวเองใช้…
13,000 Leaked Screenshots Show Why Agentic Tool Output Needs a Firewall, Not Just a Prompt Over 13,000 internal screenshots from more than 300 organizations, including Fortune 500 companies and a frontier AI lab, ended up sitting in a publicly accessible storage bucket.
Showing 18 of 49 stories
Load more storiesGet the top AI news and tools straight to your inbox every week.
Weekly · AI news from Dev.to AI
Join 15,000+ AI enthusiasts